
FTC Safeguards Rule Checkup: Is Your Dealership’s Customer Data Program Ready?
Dealerships collect a significant amount of sensitive customer information through the sales, financing, and leasing process. Credit applications, income details, Social Security numbers, account information, insurance records, and lender communications may all pass through the store before, during, and after a transaction.
That makes data protection more than an IT concern. For dealer principals, controllers, and finance leaders, the FTC Safeguards Rule is a governance and compliance issue that deserves regular attention.
The FTC has made clear that many automobile dealers are covered financial institutions under the Safeguards Rule. Dealers that finance or help arrange financing for consumers generally fall under the rule, and dealers that lease vehicles for more than 90 days may also be covered.
Why the Rule Matters for Dealership Leadership
The Safeguards Rule requires covered businesses to develop, implement, and maintain an information security program designed to protect customer information. While technology is part of that program, leadership oversight is equally important.
A dealership’s program should reflect how information actually moves through the business. That includes F&I, accounting, sales, service contracts, vendor relationships, document storage, email practices, and customer follow-up. If customer information is collected, transmitted, accessed, or retained, it should be considered within the program.
For principals and controllers, the key question is not whether the dealership has software in place. The better question is whether the dealership can demonstrate that its safeguards are documented, active, reviewed, and understood by the people who handle customer information.
Vendor Access Deserves a Closer Look
Dealerships often rely on outside providers for DMS platforms, CRM tools, marketing, financing, forms, payroll, document storage, and other services. Those relationships can create added data security responsibilities.
The FTC expects covered businesses to take steps to oversee service providers that have access to customer information. That means vendor management should not be limited to price, function, or convenience. Contracts, access rights, data-sharing practices, and security expectations all deserve periodic review.
A practical checkup may include asking who has access to customer data, whether access is still needed, how vendors protect information, and what happens if a vendor experiences a security event.
Incident Readiness Is Part of Compliance
Even strong programs need response planning. The Safeguards Rule includes expectations around detecting and responding to security events, and certain breaches involving customer information may require notice to the FTC.
Dealer leadership should understand who is responsible for response decisions, how incidents are escalated, where key records are stored, and how communication will be handled. A written plan can help reduce confusion if a data issue arises.
Make the Checkup a Business Routine
Safeguards Rule compliance should not be treated as a one-time project. Staffing changes, new systems, vendor updates, remote access, and evolving fraud risks can all affect the dealership’s data security posture.
A periodic checkup gives dealership leadership a chance to confirm that policies, procedures, vendor oversight, and employee practices still match the way the business operates. Brady Martz works with dealerships to identify business, accounting, and compliance issues that may affect operations. If your dealership arranges financing or leases vehicles, now is a good time to revisit whether your customer data program is ready for today’s expectations.
Related Posts

Year-End Tax Considerations for Dealerships: What to Review Before Closing Out 2025
As dealerships prepare to close their books for 2025, tax strategy becomes just as important as sales performance. The final weeks of the year bring opportunities to reduce tax liability, strengthen financial positions, and enter 2026 with clearer visibility and fewer surprises. But dealership tax planning is complex, with inventory rules, floorplan interest co
Preparing for Q2: Mid-Year Sales and Tax Strategies for Dealerships
As dealerships move into the second quarter, the pace of the year becomes clearer. First-quarter results often reveal trends in inventory movement, consumer demand, and margin compression that require prompt attention. A disciplined mid-year review gives dealership leaders the opportunity to refine both sales execution and tax positioning before year-end pressu
When the Supply Chain Strikes: How Auto Dealerships Can Navigate Disruption
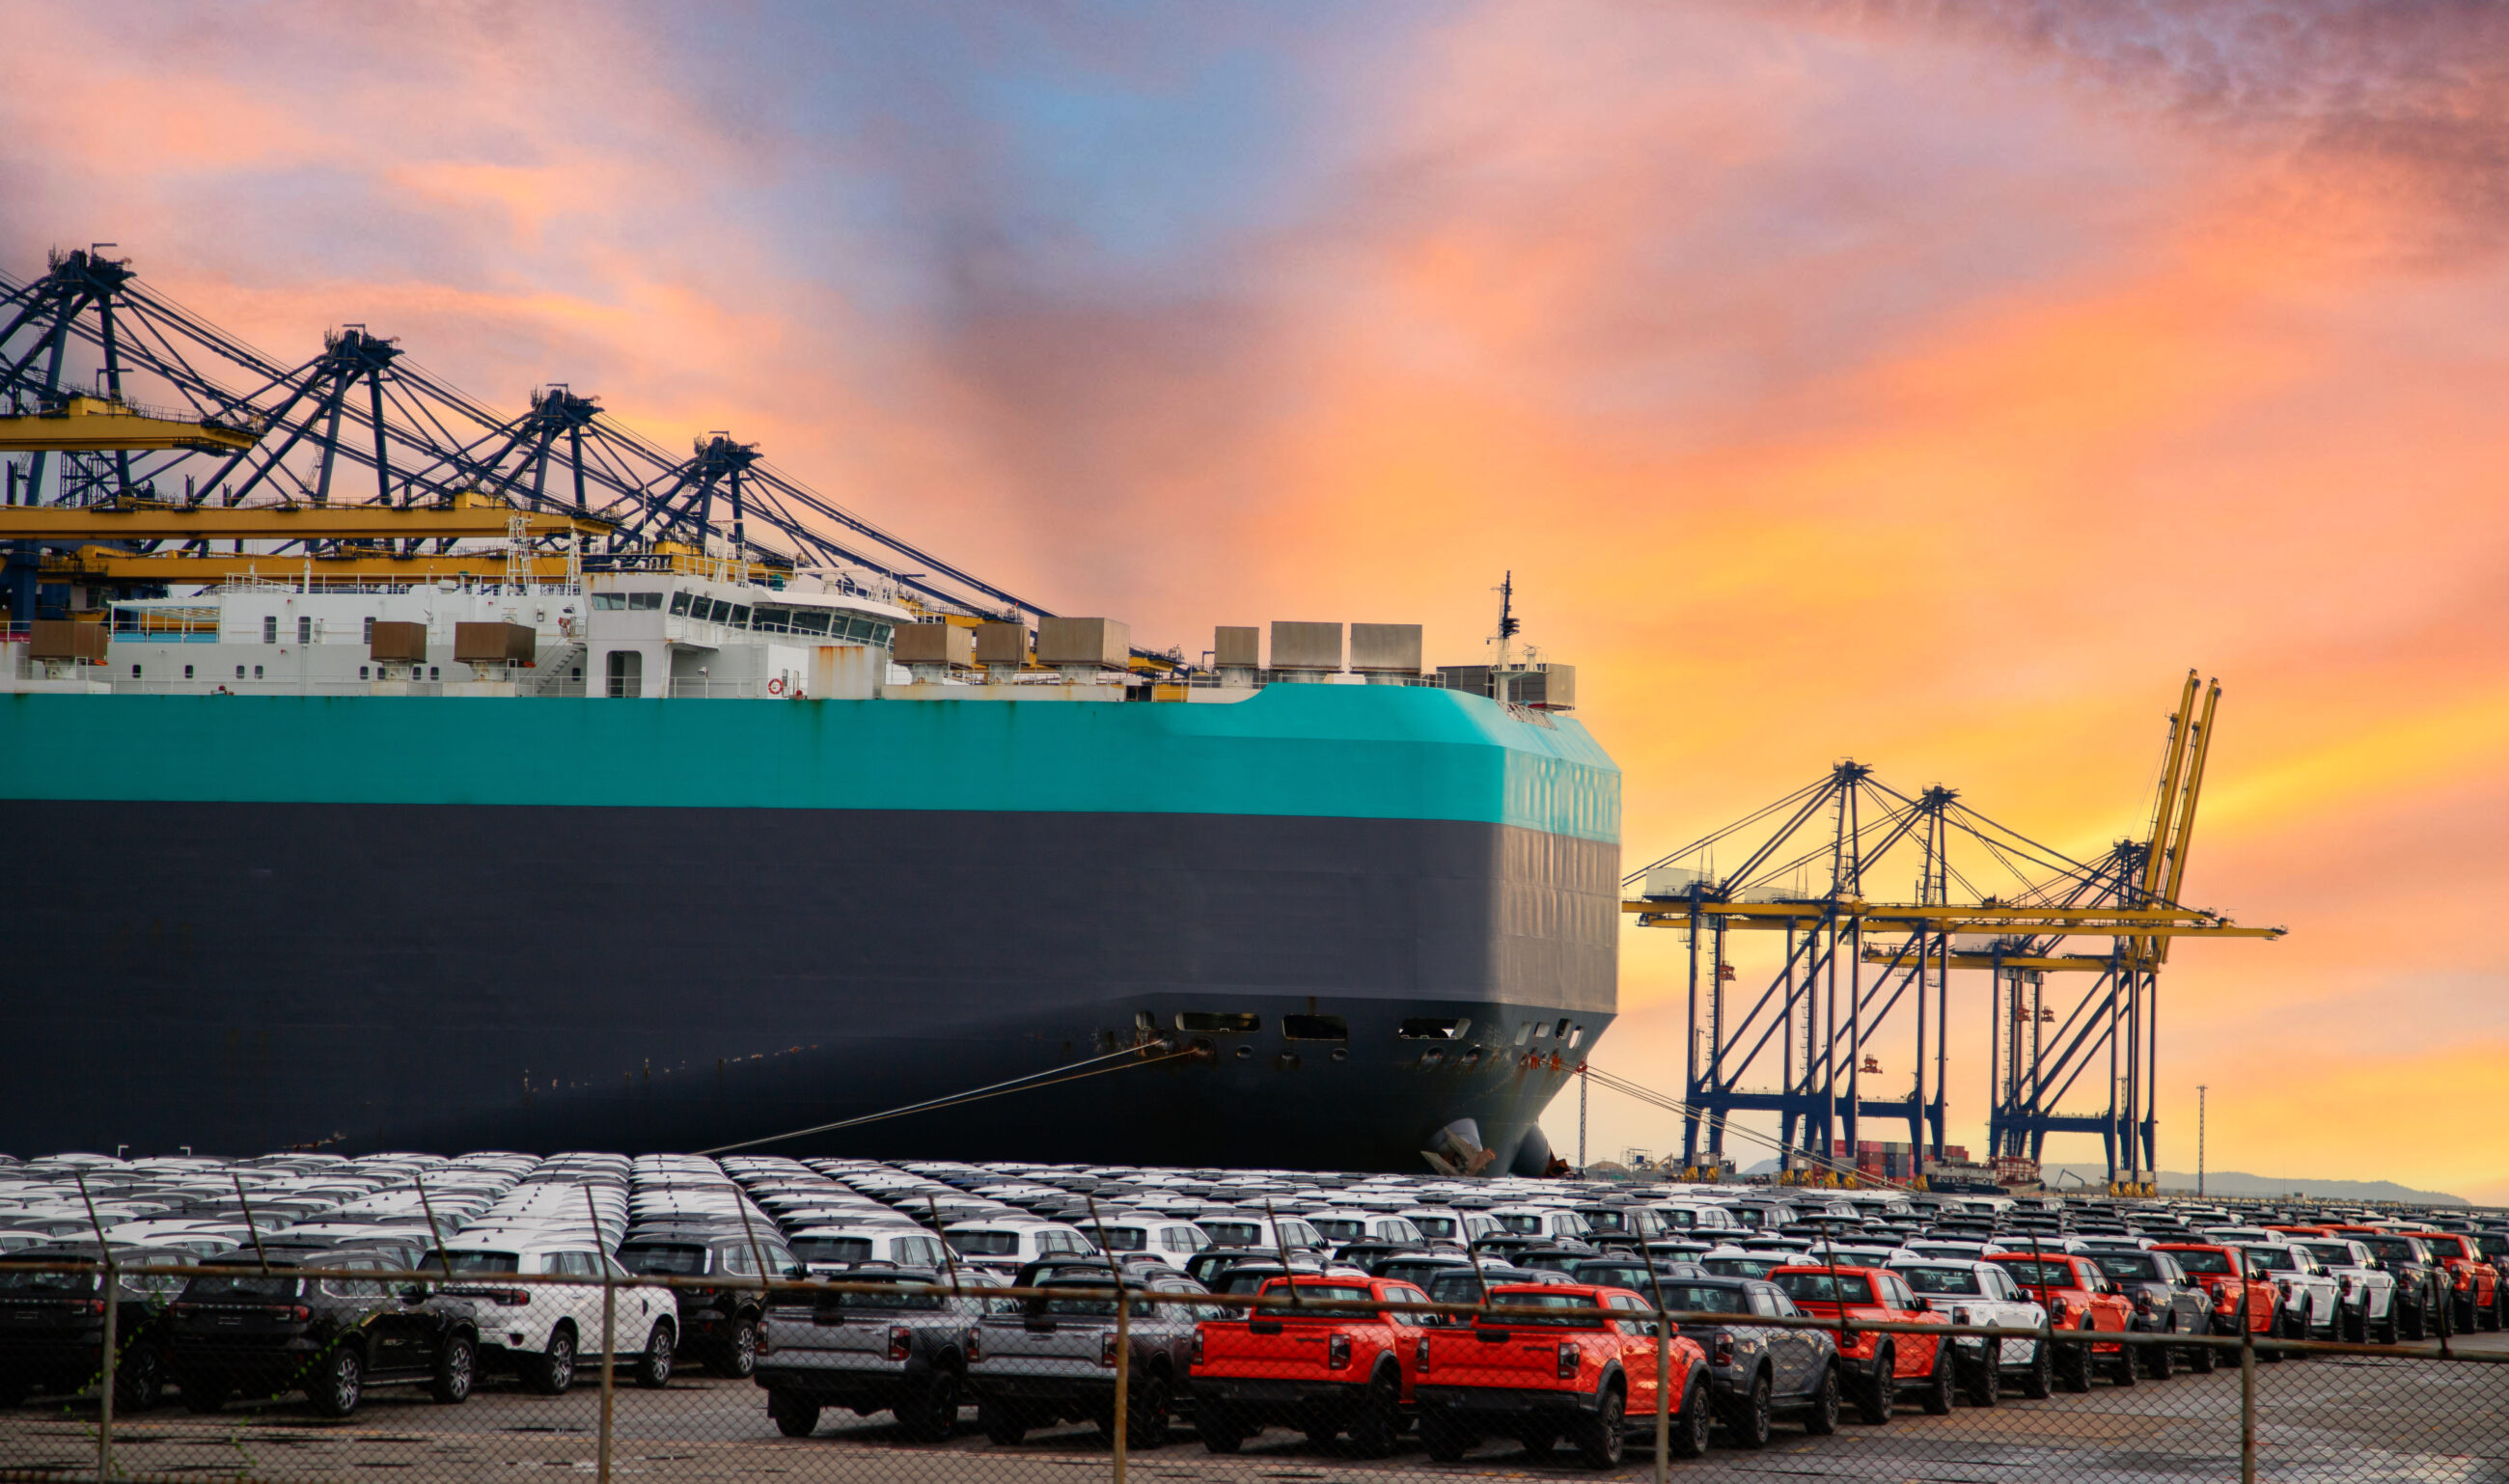
You don’t have to look far to see headlines about global supply chain strain. Between semiconductor constraints, freight bottlenecks, geopolitical shifts, and ripple effects from cyberattacks, the auto industry is navigating turbulence. For dealerships, these pressures aren’t abstract — they show up in delayed deliveries, constrained parts inventories, un
Using Data Analytics to Improve Sales Forecasting and Inventory Management
Dealerships operate in a fast-paced and constantly shifting market. From manufacturer incentives and seasonal demand changes to fluctuating interest rates and supply chain challenges, staying ahead requires more than instinct — it requires insight. One of the most valuable tools available to dealerships today is data analytics, which can significantly improve